Reduce phishing risk across engineering, customer data, and fast-moving teams.
Technology companies move fast — distributed engineering teams, cloud infrastructure, customer data, and constant tool sprawl. Trawl pairs phishing simulation, Investigation Lab training, and role-based follow-up so technical and non-technical staff alike can spot suspicious requests before source code, credentials, or customer data are put at risk.
Awareness programs work best when they reflect real engineering and tooling pressure.
Tech teams move between code repositories, cloud consoles, internal tools, and customer support — often distributed across time zones with minimal in-person verification. Attackers take advantage of that by imitating vendors, internal tools, and colleagues. Trawl connects realistic testing, training delivery, and human risk management so security teams can see which roles and tools need reinforcement — instead of relying on one all-hands security talk a year.
Tool sprawl widens the attack surface
Every SaaS login, dev tool, and cloud console is a plausible-looking phishing target — and most teams use dozens of them.
Distributed teams remove in-person checks
Remote and hybrid teams rely on Slack, email, and video calls for everything — including the requests attackers imitate.
Source code and customer data raise the stakes
A single compromised credential can expose source code, infrastructure access, or customer data — not just an inbox.
Technology threats that often begin with a trusted-looking message.
Phishing against technology companies usually succeeds when an attacker looks like a normal part of the toolchain. These scenarios deserve extra attention.
- Dev-tool and SaaS impersonation
Fake GitHub, Slack, AWS, or Google Workspace alerts are common lures into credential-harvesting pages. - Credential theft against internal systems
Fake SSO and re-authentication prompts are a frequent path into source code, infrastructure, and admin tools. - Vendor and colleague impersonation
Attackers spoof coworkers, contractors, or SaaS vendors to pressure staff into approving access or payments. - Malicious attachments disguised as work documents
Invoices, contracts, and onboarding files are mimicked to create believable lures for admin and support staff. - Urgency-driven social engineering
Fast-moving teams are primed to act on urgent requests — exactly the pressure attackers rely on.
Tie realistic phishing tests to faster remediation and clearer risk visibility.
The Trawl phishing simulator runs scenarios tied to SSO re-authentication, dev-tool notifications, and vendor requests — so the program stays useful, instead of resembling generic tests that never resemble actual engineering workflows. After a failure, Investigation Lab walks the exact message back apart — sender, domain, links, and social-engineering indicators — the same way a security team would.
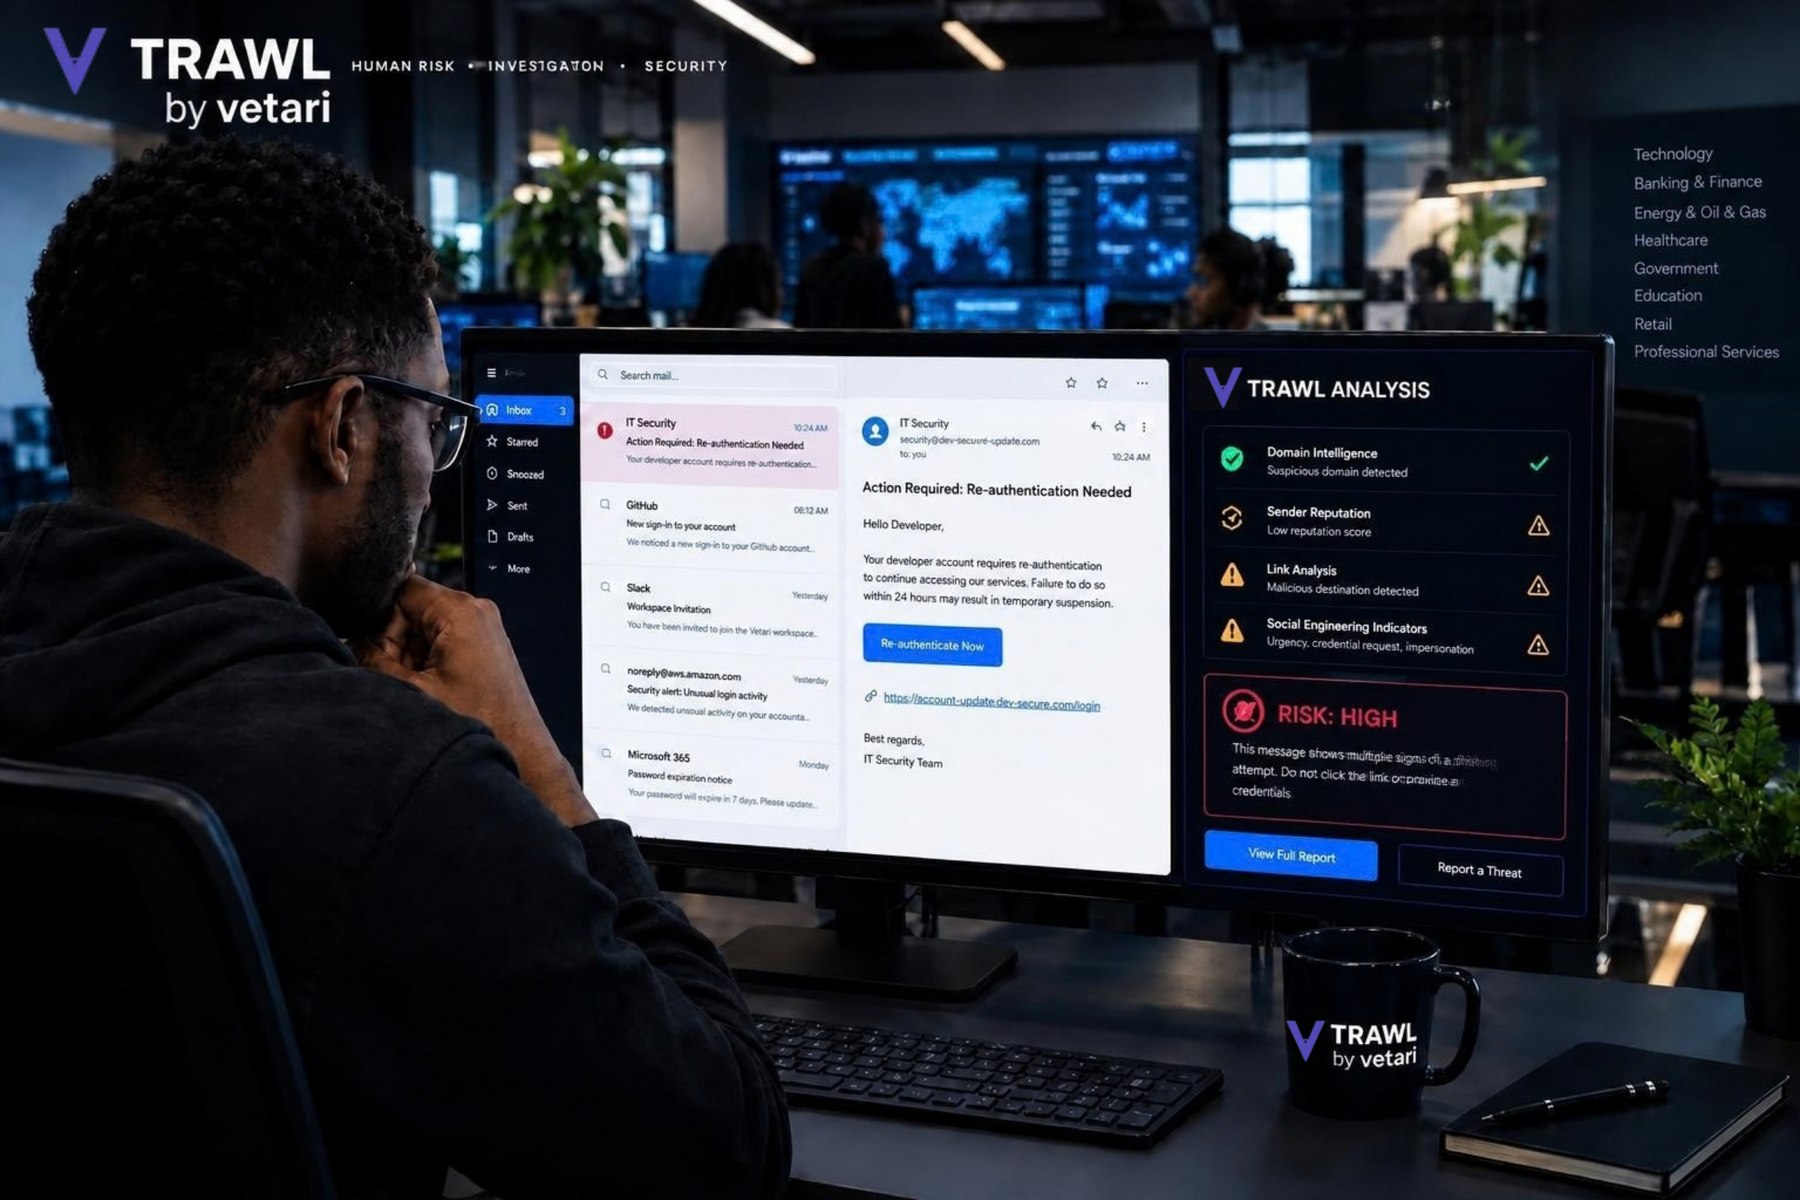
The Human Risk Dashboard then helps identify repeat behavior, compare teams, and focus attention on the roles most likely to create downstream exposure — engineering, support, and admin alike.
Train the roles closest to code, infrastructure, and customer data.
Engineers, support staff, admins, and finance all see different versions of phishing. The best technology-company programs make those examples specific instead of relying on generic awareness content.
Use security awareness training to reinforce how staff should handle unusual requests around access, credentials, and vendor payments. Those lessons stick harder when they match the real tools teams already use.
- Prioritize engineering and infrastructure access — the downside of one compromised credential is immediate, which makes these ideal candidates for extra testing
- Support customer-facing and support teams — frontline staff deal with urgent, trust-based communication daily
- Keep finance and admin in scope — vendor and payment impersonation targets these roles directly
Strengthen awareness across engineering & support workflows.
Trawl helps technology companies reduce phishing risk across engineering, support, admin, and customer-facing teams.
Request a demo View pricingRecommended technology resources.
Use these to support internal awareness planning and frame phishing risk in engineering and operational terms.
What is the phishing failure rate by industry?
Benchmark phishing performance across sectors and use that context in leadership conversations.
The cost of a phishing attack
Connect phishing exposure to financial loss and operational disruption — useful for building the case for testing budget.
Phishing facts and statistics
Use current phishing data to support awareness budgeting, program design, and recurring executive reporting.
Phishing training
Connect phishing failures to training moments and follow-up coaching for technology teams.
Explore training →